# Deny certain subnets when advertising 0.0.0.0/0
**URL:** https://forum.pritunl.com/t/deny-certain-subnets-when-advertising-0-0-0-0-0/626
**Category:** Pritunl VPN
**Created:** [December 15, 2022, 9:59am UTC](https://forum.pritunl.com/t/deny-certain-subnets-when-advertising-0-0-0-0-0/626 "2022-12-15T09:59:20Z")
**Posts on this page:** 4
**Page:** 1
### Author:  [@fmalykh](https://forum.pritunl.com/u/fmalykh)
#### Post date: [December 15, 2022, 9:59am UTC](https://forum.pritunl.com/t/deny-certain-subnets-when-advertising-0-0-0-0-0/626/1 "2022-12-15T09:59:20Z")
Hi,
When advertising default to a client, we need to restrict access to some subnets.
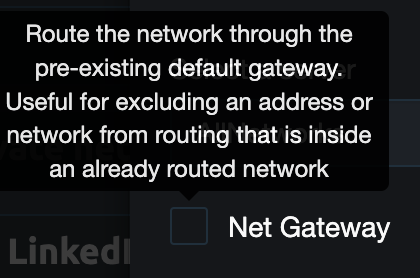
Can this feature be enhanced to create pritunl server iptables rule denying traffic to subnets marked as Net Gateway?
---
### Author:  [@zach](https://forum.pritunl.com/u/zach)
#### Post date: [December 16, 2022, 3:53am UTC](https://forum.pritunl.com/t/deny-certain-subnets-when-advertising-0-0-0-0-0/626/2 "2022-12-16T03:53:17Z")
Net gateway does not block access, it only instructs the client to route that subnet through the default gateway. The client can ignore that route instruction, WireGuard connections also currently ignore all net gateway routes. This should be done with a firewall instead.
---
### Author:  [@fmalykh](https://forum.pritunl.com/u/fmalykh)
#### Post date: [December 16, 2022, 6:55am UTC](https://forum.pritunl.com/t/deny-certain-subnets-when-advertising-0-0-0-0-0/626/3 "2022-12-16T06:55:16Z")
This is clear.
What I’m asking is a feature request to deny certain subnets as a part of server configuration when adevertising default / other supernets.
This is problematic to achieve with firewall when NAT is enabled in Pritunl for VPC-peered AWS environments which can’t be transitive.
---
### Author:  [@zach](https://forum.pritunl.com/u/zach)
#### Post date: [December 16, 2022, 5:06pm UTC](https://forum.pritunl.com/t/deny-certain-subnets-when-advertising-0-0-0-0-0/626/4 "2022-12-16T17:06:57Z")
There isn’t any plans on changing the available routing options currently.