# How to install the pritunl client on Fedora Silverblue?
**URL:** https://forum.pritunl.com/t/how-to-install-the-pritunl-client-on-fedora-silverblue/3624
**Category:** Pritunl VPN
**Created:** [November 11, 2025, 10:49pm UTC](https://forum.pritunl.com/t/how-to-install-the-pritunl-client-on-fedora-silverblue/3624 "2025-11-11T22:49:47Z")
**Posts on this page:** 8
**Page:** 1
### Author:  [@sec\_op](https://forum.pritunl.com/u/sec_op)
#### Post date: [November 11, 2025, 10:49pm UTC](https://forum.pritunl.com/t/how-to-install-the-pritunl-client-on-fedora-silverblue/3624/1 "2025-11-11T22:49:47Z")
Hi,
Due to several reasons we are using Fedora Silverblue in our company. We would like to switch to Pritunl however, I did not find any information in your website on installing Pritunl on Fedora Silverblue!
It would be great if you would be able to publish your client on Flathub for example, so that we can easily install your client from any distro.
---
### Author:  [@zach](https://forum.pritunl.com/u/zach)
#### Post date: [November 12, 2025, 4:07am UTC](https://forum.pritunl.com/t/how-to-install-the-pritunl-client-on-fedora-silverblue/3624/2 "2025-11-12T04:07:30Z")
There’s currently no plans on packaging it on Flathub. A [**custom build system**](https://github.com/pacur/pacur) is used to package all the Pritunl software for Linux and it would require significant changes to add Flathub support.
If you only want the CLI it only requires Go. This can be built and installed using the commands below. The build process for the GUI version is more complex, the build file is available in the [**pritunl/pritunl-pacur**](https://github.com/pritunl/pritunl-pacur/blob/master/pritunl-client-electron/PKGBUILD) repository.
```bash
sudo dnf -y install git-core golang openvpn wireguard-tools
GOPATH="~/go" go install -v github.com/pritunl/pritunl-client-electron/service@latest
GOPATH="~/go" go install -v github.com/pritunl/pritunl-client-electron/cli@latest
sudo cp /home/cloud/go/bin/service /usr/local/bin/pritunl-client-service
sudo cp /home/cloud/go/bin/cli /usr/local/bin/pritunl-client
sudo tee /etc/systemd/system/pritunl-client.service << EOF
[Unit]
Description=Pritunl Client Daemon
[Service]
ExecStart=/usr/local/bin/pritunl-client-service
[Install]
WantedBy=multi-user.target
EOF
sudo systemctl daemon-reload
sudo systemctl enable --now pritunl-client
```
---
### Author:  [@sec\_op](https://forum.pritunl.com/u/sec_op)
#### Post date: [November 13, 2025, 1:41pm UTC](https://forum.pritunl.com/t/how-to-install-the-pritunl-client-on-fedora-silverblue/3624/3 "2025-11-13T13:41:06Z")
Thank you for your reply.
That is the problem here, Fedora Silverblue does not use DNF package manager.
It has a layered package manager called rpm-ostree. This is really sad to see it. Immutable distros are great for Enterprise environments. Then we should be looking for an alternative solution.
Thank you anyways.
---
### Author:  [@zach](https://forum.pritunl.com/u/zach)
#### Post date: [November 13, 2025, 4:51pm UTC](https://forum.pritunl.com/t/how-to-install-the-pritunl-client-on-fedora-silverblue/3624/4 "2025-11-13T16:51:06Z")
I may in the future start using Flatpak and then start publishing packages to it. The Pritunl Client requires a background service with system network access. It would require extensive changes to the client to run inside a Flatpak container.
But the issue with almost all Flatpak packages and Flatpak in general is without extensive changes it isn’t really achieving any additional system security. Almost all the packages have nearly the same permissions the software would have before Flatpak. I started running desktop software in containers and Xephyr 10 years ago with [**custom scripts**](https://github.com/dockercask/dockercask). But desktop performance and virtualization has improved significantly since then and I transitioned to isolating software into QEMU/KVM virtual machines. I currently run a RHEL 10 desktop with 6 Fedora virtual machines using [**Pritunl Cloud**](https://cloud.pritunl.com/), a [**QEMU GTK build**](https://github.com/pritunl/qemu-build) and [**clipboard sharing**](https://github.com/zachhuff386/clipsync). This provides true isolation between different groups of software and required file access.
---
### Author:  [@sec\_op](https://forum.pritunl.com/u/sec_op)
#### Post date: [November 14, 2025, 10:32am UTC](https://forum.pritunl.com/t/how-to-install-the-pritunl-client-on-fedora-silverblue/3624/5 "2025-11-14T10:32:58Z")
I completely understand your point.
Having VPN clients to work as a Flatpak package is not that easy.
We are also using Mullvad for instance, and for Mullvad we found a solution on this website:
> **[How to install Mullvad VPN on Fedora Silverblue? - PC Forum Guides, Reviews...](https://pcforum.org/wiki/entry/12-how-to-install-mullvad-vpn-on-fedora-silverblue/)**
>
> Here we explain how to install Mullvad VPN on Fedora Silverblue Linux using rpm-ostree.
Of course it is not the cleanest way. Because for each update we have to remove the software, reboot, and then install it again. But it works!
If you can offer such a solution till you move to a Flatpack package, it would be great. In Fedora Silverblue, repositories are completely removed from the package manager. Therefore, we can only install .rpm files as it is explained in the above website. So I think it would be great if you can publish the .rpm file in addition to the repo so that we can test it.
I also noticed an another issue, I am not sure if this is the right topic to talk about it. When we connect to the VPN via WireGuard, our main DNS is still leaking. Could you please recommend a way to avoid it? Maybe I have missed something in the configurations.
Thank you for your support.
---
### Author:  [@zach](https://forum.pritunl.com/u/zach)
#### Post date: [November 14, 2025, 2:59pm UTC](https://forum.pritunl.com/t/how-to-install-the-pritunl-client-on-fedora-silverblue/3624/6 "2025-11-14T14:59:13Z")
There are still a lot of DNS configurations that don’t work on Linux. It will depend on the support of what DNS system the Linux distribution is using.
Check that the DNS server is shown in `sudo cat /etc/wireguard/wg0.conf` and verify the DNS server is included in the server routes.
---
### Author:  [@p-hash](https://forum.pritunl.com/u/p-hash)
#### Post date: [April 7, 2026, 1:50pm UTC](https://forum.pritunl.com/t/how-to-install-the-pritunl-client-on-fedora-silverblue/3624/7 "2026-04-07T13:50:58Z")
I was able to successfully install Pritunl CLI on bluefin-gdx:lts. I chose CLI client because it is static go binary and does not depend on electron and nodejs like GUI client, but if you need GUI, I think `pritunl-client-electron` should work as well
`sudo tee /etc/yum.repos.d/pritunl.repo << EOF`
`[pritunl]`
`name=Pritunl Stable Repository`
`baseurl=https://repo.pritunl.com/stable/yum/fedora/43/`
`gpgcheck=1`
`enabled=1`
`gpgkey=https://raw.githubusercontent.com/pritunl/pgp/master/pritunl_repo_pub.asc`
`EOF`
`sudo rpm-ostree install pritunl-client`
After reboot, I had to start the service:
`sudo systemctl enable --now pritunl-client`
When service started, I was able to connect (this time running commands as regular user, not root):
`pritunl-client list # gives empty list`
`pritunl-client add pritunl://demo.pritunl.com/ku/rBCDSgw5`
`pritunl-client list # gives single entry with id`
`pritunl-client start `
> **[Command Line Interface](https://docs.pritunl.com/docs/command-line-interface)**
>
> Pritunl command line interface usage
---
### Author:  [@zach](https://forum.pritunl.com/u/zach)
#### Post date: [September 5, 2026, 2:09pm UTC](https://forum.pritunl.com/t/how-to-install-the-pritunl-client-on-fedora-silverblue/3624/8 "2026-09-05T14:09:52Z")
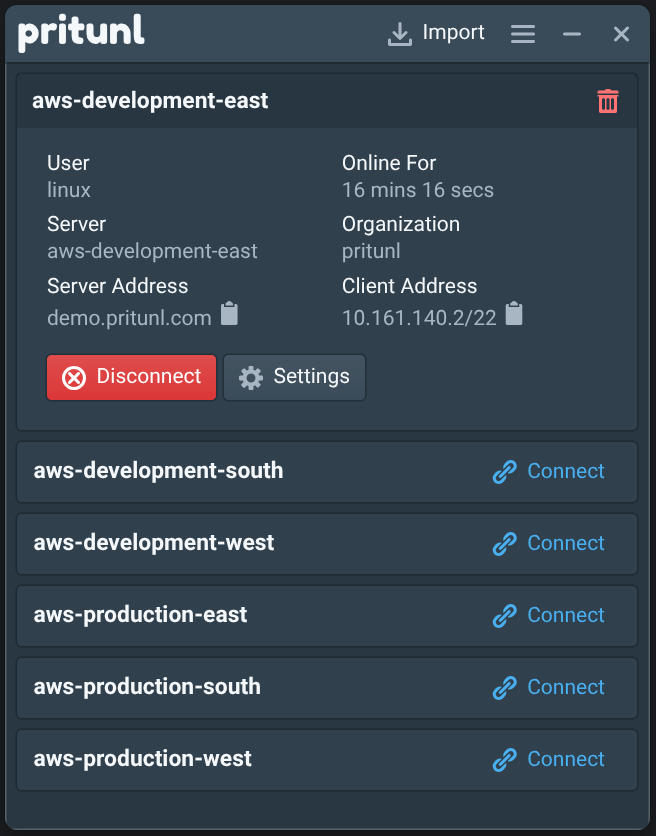
This has been added is now available in the repo at [**pritunl/pritunl-client/flatpak**](https://github.com/pritunl/pritunl-client/tree/master/flatpak). The Flatpak client runs without root using NetworkManager and supports WireGuard connections. OpenVPN connections are currently not supported. The next release should be published to a Flatpak repo at `repo.pritunl.com/stable/flatpak`. The commands below will locally build and run the Flatpak client.
```bash
git clone https://github.com/pritunl/pritunl-client.git
cd pritunl-client/flatpak
rm -rf .flatpak-builder/ build-dir/
flatpak run org.flatpak.Builder --user --install --force-clean --disable-rofiles-fuse build-dir com.pritunl.Client.local.yml
flatpak run com.pritunl.Client
```