# IPSEC site to site on multiple aws accounts
**URL:** https://forum.pritunl.com/t/ipsec-site-to-site-on-multiple-aws-accounts/858
**Category:** Pritunl VPN
**Tags:** pritunl-link, pritunl
**Created:** [March 14, 2023, 11:00pm UTC](https://forum.pritunl.com/t/ipsec-site-to-site-on-multiple-aws-accounts/858 "2023-03-14T23:00:40Z")
**Posts on this page:** 5
**Page:** 1
### Author:  [@willb0t](https://forum.pritunl.com/u/willb0t)
#### Post date: [March 14, 2023, 11:00pm UTC](https://forum.pritunl.com/t/ipsec-site-to-site-on-multiple-aws-accounts/858/1 "2023-03-14T23:00:40Z")
In the directions for IPSEC Site to Site in AWS how can I handle
_AWS_ and set the access key and secret key to `role`
> **[Site-to-Site with IPsec](https://docs.pritunl.com/docs/pritunl-link)**
>
> Create a site-to-site connection between AWS, Google Cloud and Oracle Cloud
How can I deal multiple aws account when there is only space for one access key and secrete or is there another way to connect my multiple accounts?
---
### Author:  [@zach](https://forum.pritunl.com/u/zach)
#### Post date: [March 16, 2023, 5:59pm UTC](https://forum.pritunl.com/t/ipsec-site-to-site-on-multiple-aws-accounts/858/2 "2023-03-16T17:59:18Z")
For pritunl-link the access key would be set on the pritunl-link client using the command shown in that documentation. The key in the Pritunl web console is for the route advertisements on VPN servers. The Pritunl server does not function as a link client. Every link must have at least two locations and one host in each location. The pritunl-link client should not be run on the same instance as a Pritunl server.
---
### Author:  [@willb0t](https://forum.pritunl.com/u/willb0t)
#### Post date: [April 4, 2023, 8:59pm UTC](https://forum.pritunl.com/t/ipsec-site-to-site-on-multiple-aws-accounts/858/3 "2023-04-04T20:59:34Z")
> [@zach](#):
>
> and shown in that documentation. The key in the Pritunl web console is for the route advertisements
I have two separate ec2 instance running pritunl-link, besides the primary pritunl vpn server
---
### Author:  [@willb0t](https://forum.pritunl.com/u/willb0t)
#### Post date: [April 13, 2023, 12:17am UTC](https://forum.pritunl.com/t/ipsec-site-to-site-on-multiple-aws-accounts/858/4 "2023-04-13T00:17:51Z")
> [@willb0t](#):
>
> separate ec2 instance running pritu
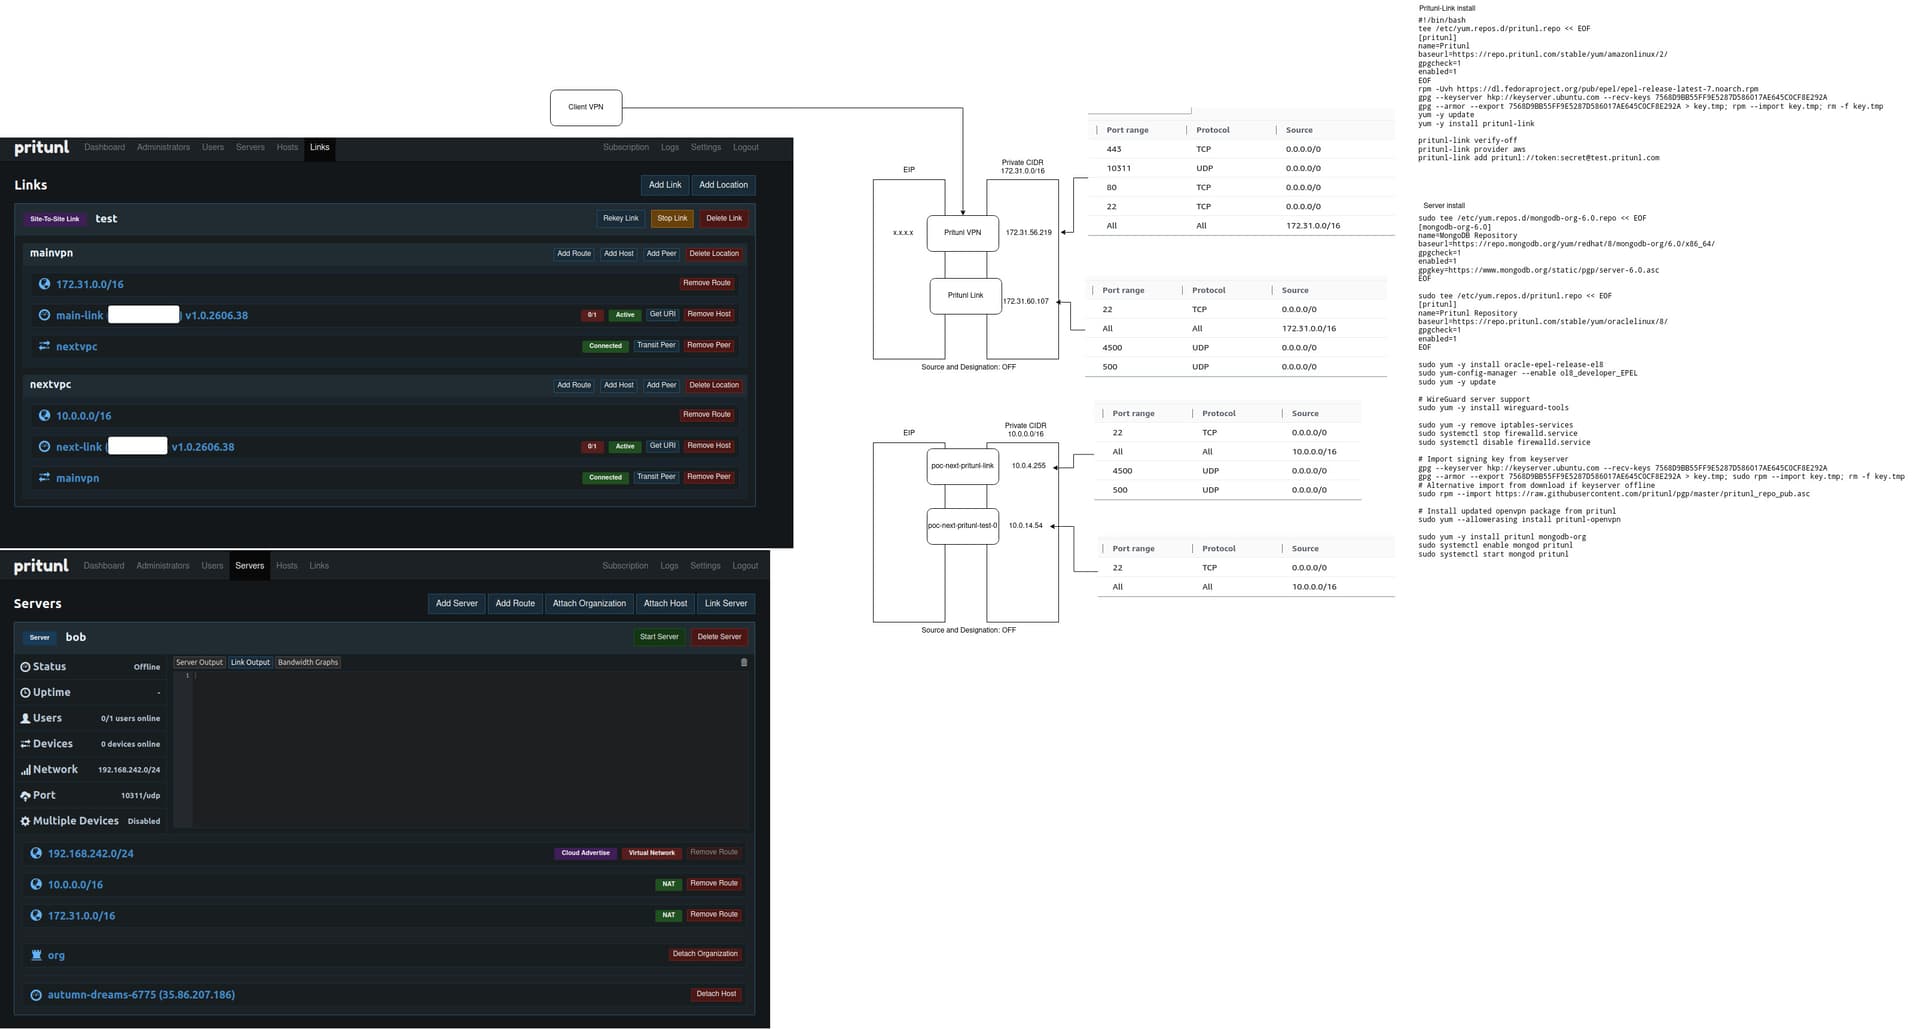
having followed [Site-to-Site with IPsec](https://docs.pritunl.com/docs/pritunl-link)
and modifying it a tad to match my needs, I am unable to route traffic over the pritunl-link.
When I was creating the pritunl-link it automatically created peer unlike in the document and when I deleted it and tested the “ipsec statusall” there was no peer so I added it back in and it now has a state of interlink latency disconnected and there are nothing in /var/logs for pritunl-link.
How can I get traffic from my vpn client to the poc-next-pritunl-link subnet?
thanks
---
### Author:  [@zach](https://forum.pritunl.com/u/zach)
#### Post date: [April 13, 2023, 6:09pm UTC](https://forum.pritunl.com/t/ipsec-site-to-site-on-multiple-aws-accounts/858/5 "2023-04-13T18:09:36Z")
That configuration should not have cloud advertised enabled for the virtual network. The routes are using NAT and the virtual network is not available to the link.
Verify the firewalls are configured correctly on each VPC to accept traffic from the other VPC.